Choose what this site may store in your browser. You can change this at any time from the footer.

DevSecOps AIOps services

Software-delivery reliability, AppSec prioritization, supply-chain protection and secure release automation.

Talk to a DevSecOps AIOps Specialist
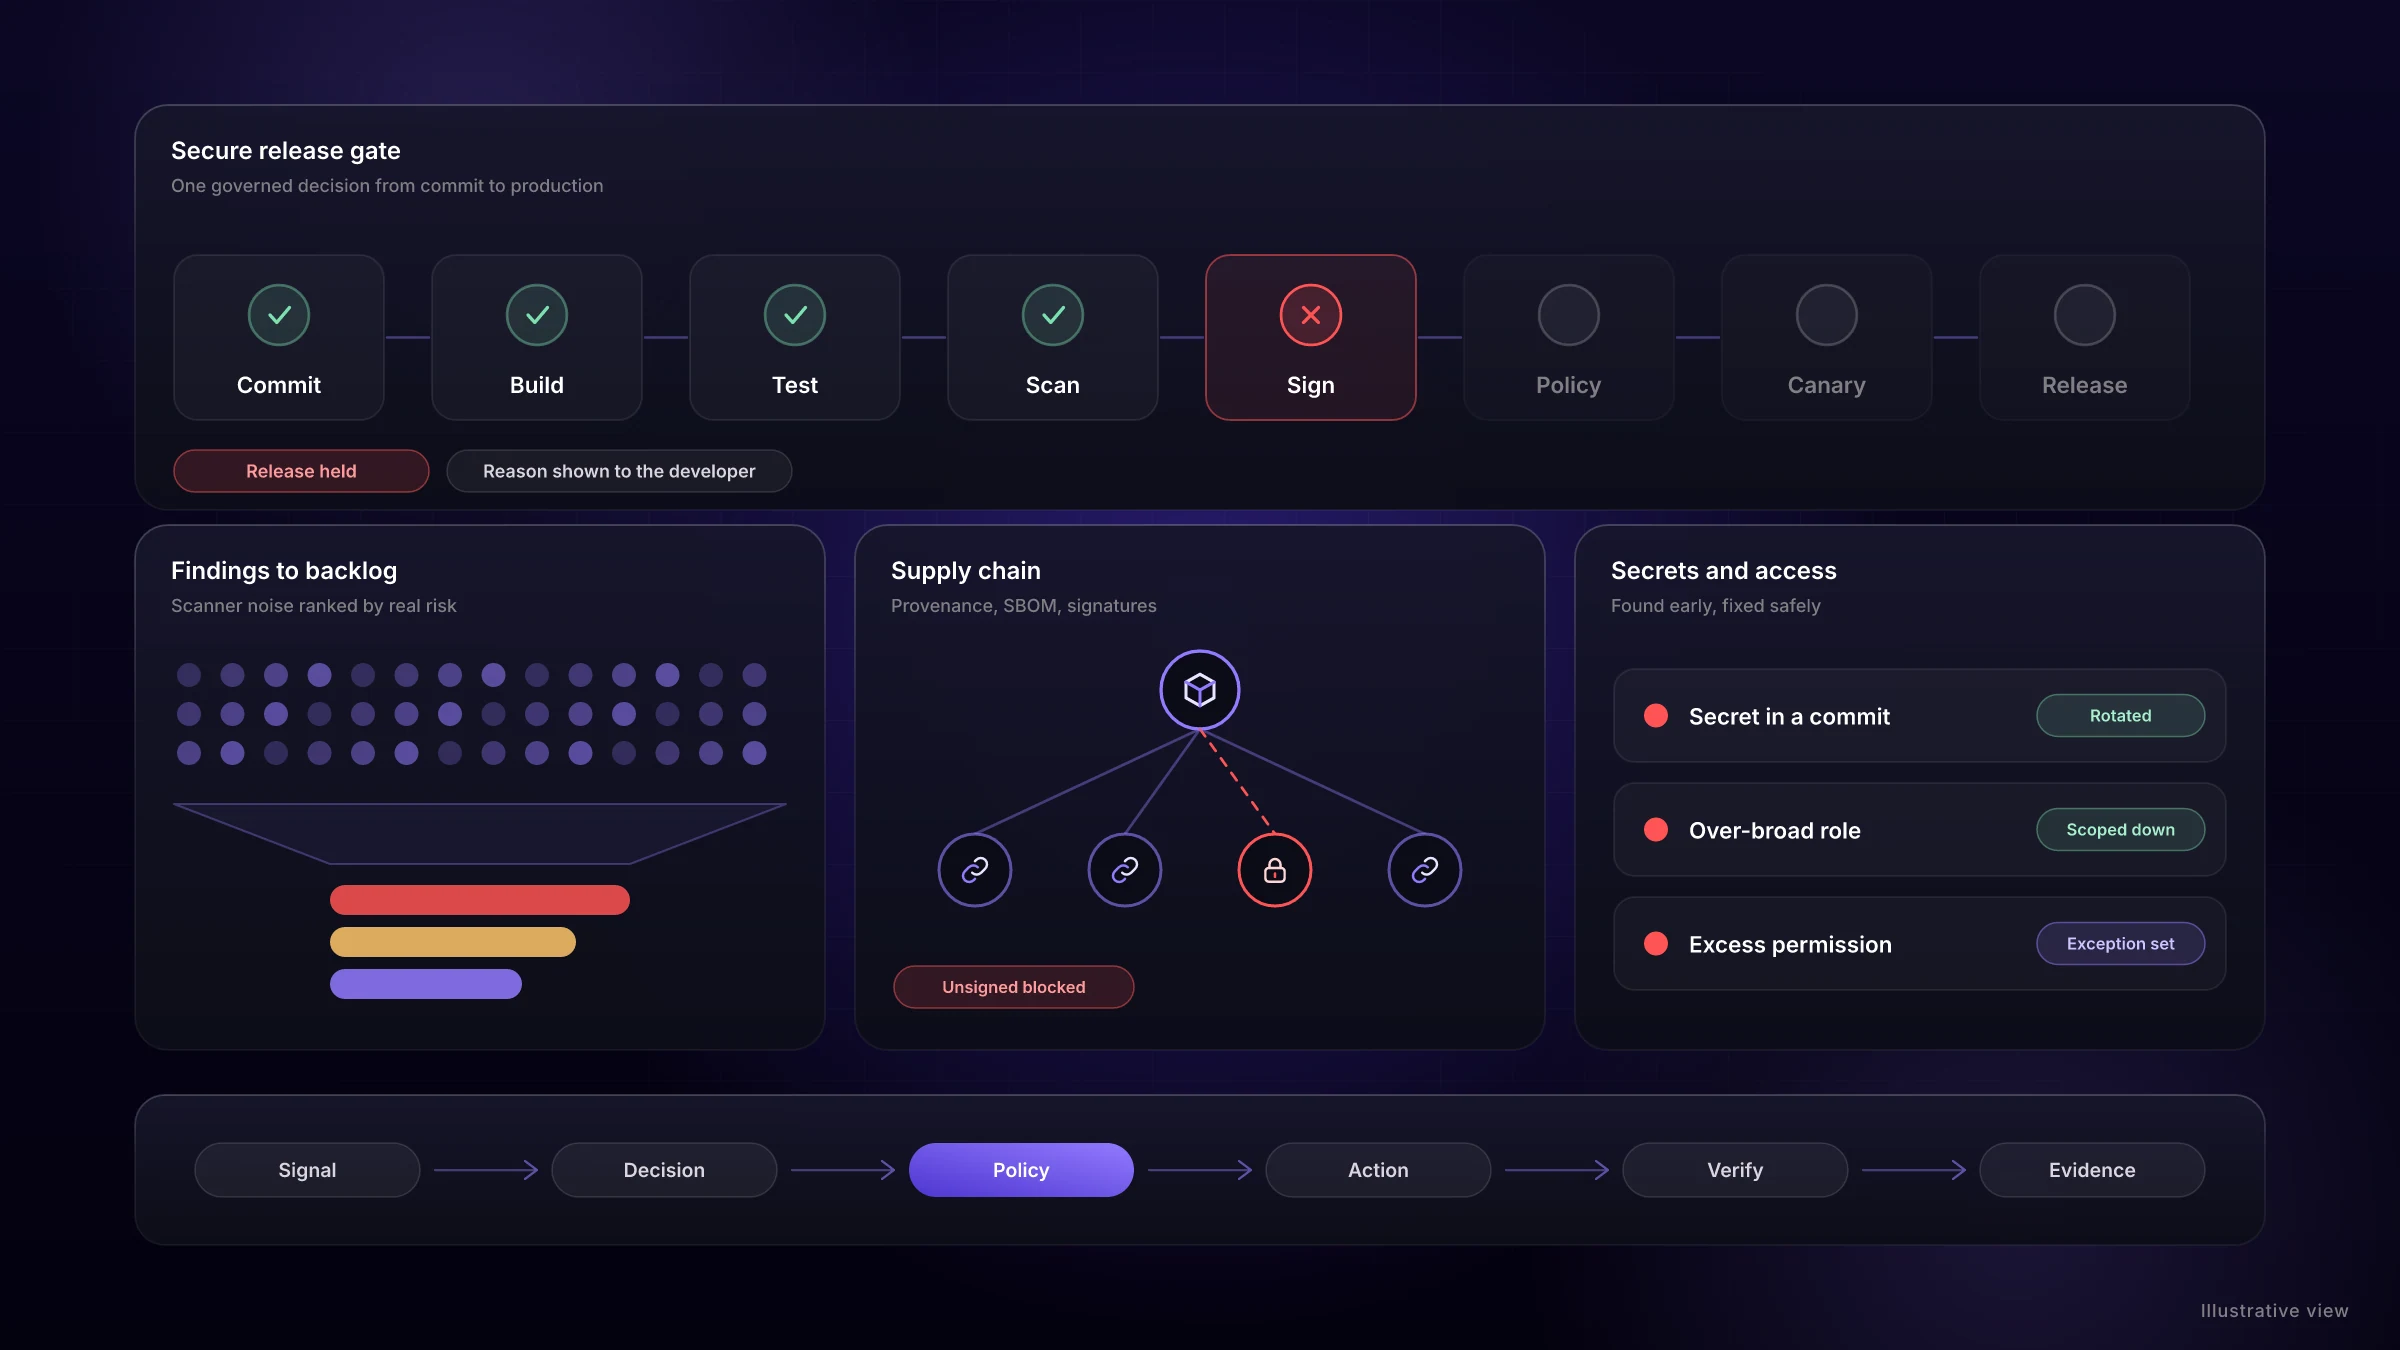
Illustrative view: a release pipeline held at an unsigned artifact, scanner findings ranked into a short backlog, a supply-chain tree and secret and access fixes

Five DevSecOps AIOps services

Each service can be taken alone. They share telemetry, policy and runbooks when combined.

CI/CD Pipeline Reliability & Root Cause

Classify pipeline failures, spot flaky and transient issues and recommend safe recovery.

Example scenario

Trigger different pipeline failures and show classification plus a safe retry.

Core capabilities

  • Pipeline telemetry
  • Failure taxonomy
  • Log summarization
  • Flaky-test detection
  • Duration anomalies
  • Root-cause analysis

Application Security Risk Prioritization

Deduplicate and rank SAST, DAST, dependency, container and IaC findings by exploitability and context.

Example scenario

Ingest several scanner outputs and produce one prioritized developer backlog.

Core capabilities

  • Multi-scanner ingestion
  • Deduplication
  • Reachability and context
  • Risk ranking
  • Ownership
  • SLA

Software Supply Chain Security

Track SBOMs, provenance, artifact signatures, dependencies and build integrity.

Example scenario

Introduce an unapproved dependency or unsigned artifact and block the build.

Core capabilities

  • SBOM ingestion
  • Provenance verification
  • Dependency graph
  • Artifact policy
  • Signatures
  • Dashboard

Secure Release Orchestration

Combine tests, security, IaC policy, live SLO health and change risk into one governed release gate.

Example scenario

Compare a healthy release with a risky one and show different promotion outcomes.

Core capabilities

  • Release scorecard
  • Policy gate
  • Canary
  • Security gate
  • Change risk
  • Approvals

Secrets, IAM & Access Misconfiguration Prevention

Find exposed secrets and excessive permissions across code, CI/CD, Kubernetes and cloud configuration.

Example scenario

Commit a fake secret and a broad RBAC change, then detect and safely remediate both.

Core capabilities

  • Secret scanning
  • IAM diff
  • RBAC analysis
  • Least privilege
  • Exceptions
  • Access-risk timeline

What you receive

Every service is built as a local-first lab, then extended to your private cloud and to AWS, Azure or GCP.

KPI dashboards

Ingestion health, processing latency, decisions, automation success and failure, overrides and false positives where measurable.

Runbooks and policies

Validated, allowlisted actions with approval rules and least-privilege identities.

Failure-path tests

Healthy, false-positive, policy-blocked, automation-failure, rollback and telemetry-source-failure cases, all exercised.

Audit evidence and demo

Retained evidence for every decision, a short demo script, and setup, troubleshooting and cleanup documentation.

Automation with guardrails, not blind trust

Rules every AIOps action follows, in every track.

Allowlisted actions only

AI output never goes straight to a shell, cloud API or cluster. It selects from validated runbooks.

Approval for high-risk change

Disruptive actions wait for a person. Low-risk, reversible steps can run on their own once you agree the rule.

Verified outcomes

Every action is followed by a health check, with rollback or compensation when the check fails.

Complete audit history

Signals, scores, model or rule versions, approvals and results are retained and reviewable.

Typical technology base

  • OpenTelemetry
  • Prometheus
  • Grafana
  • Loki / Tempo
  • Kubernetes
  • Helm
  • Terraform
  • Ansible
  • Argo CD / Rollouts
  • Python / FastAPI
  • PostgreSQL
  • Redis / NATS / Kafka
  • Trivy · Semgrep · Checkov

Adapted to the tools you already run.

Other AIOps tracks

Combine tracks to share telemetry, policy and runbooks.

Start with DevSecOps AIOps?

Tell us what you run and where operations hurt most. We will suggest where to begin.

Talk to an AIOps Specialist

Stay in the loop

Blog posts, our newsletter and service updates on cloud migration, DevOps and reliability engineering, straight to your inbox.

We email you once to confirm. No spam, and we never share your address. Privacy Policy