Choose what this site may store in your browser. You can change this at any time from the footer.

Cybersecurity AIOps services

AI-assisted threat detection, security-event correlation, behavioral analytics and governed response.

Talk to a Cybersecurity AIOps Specialist
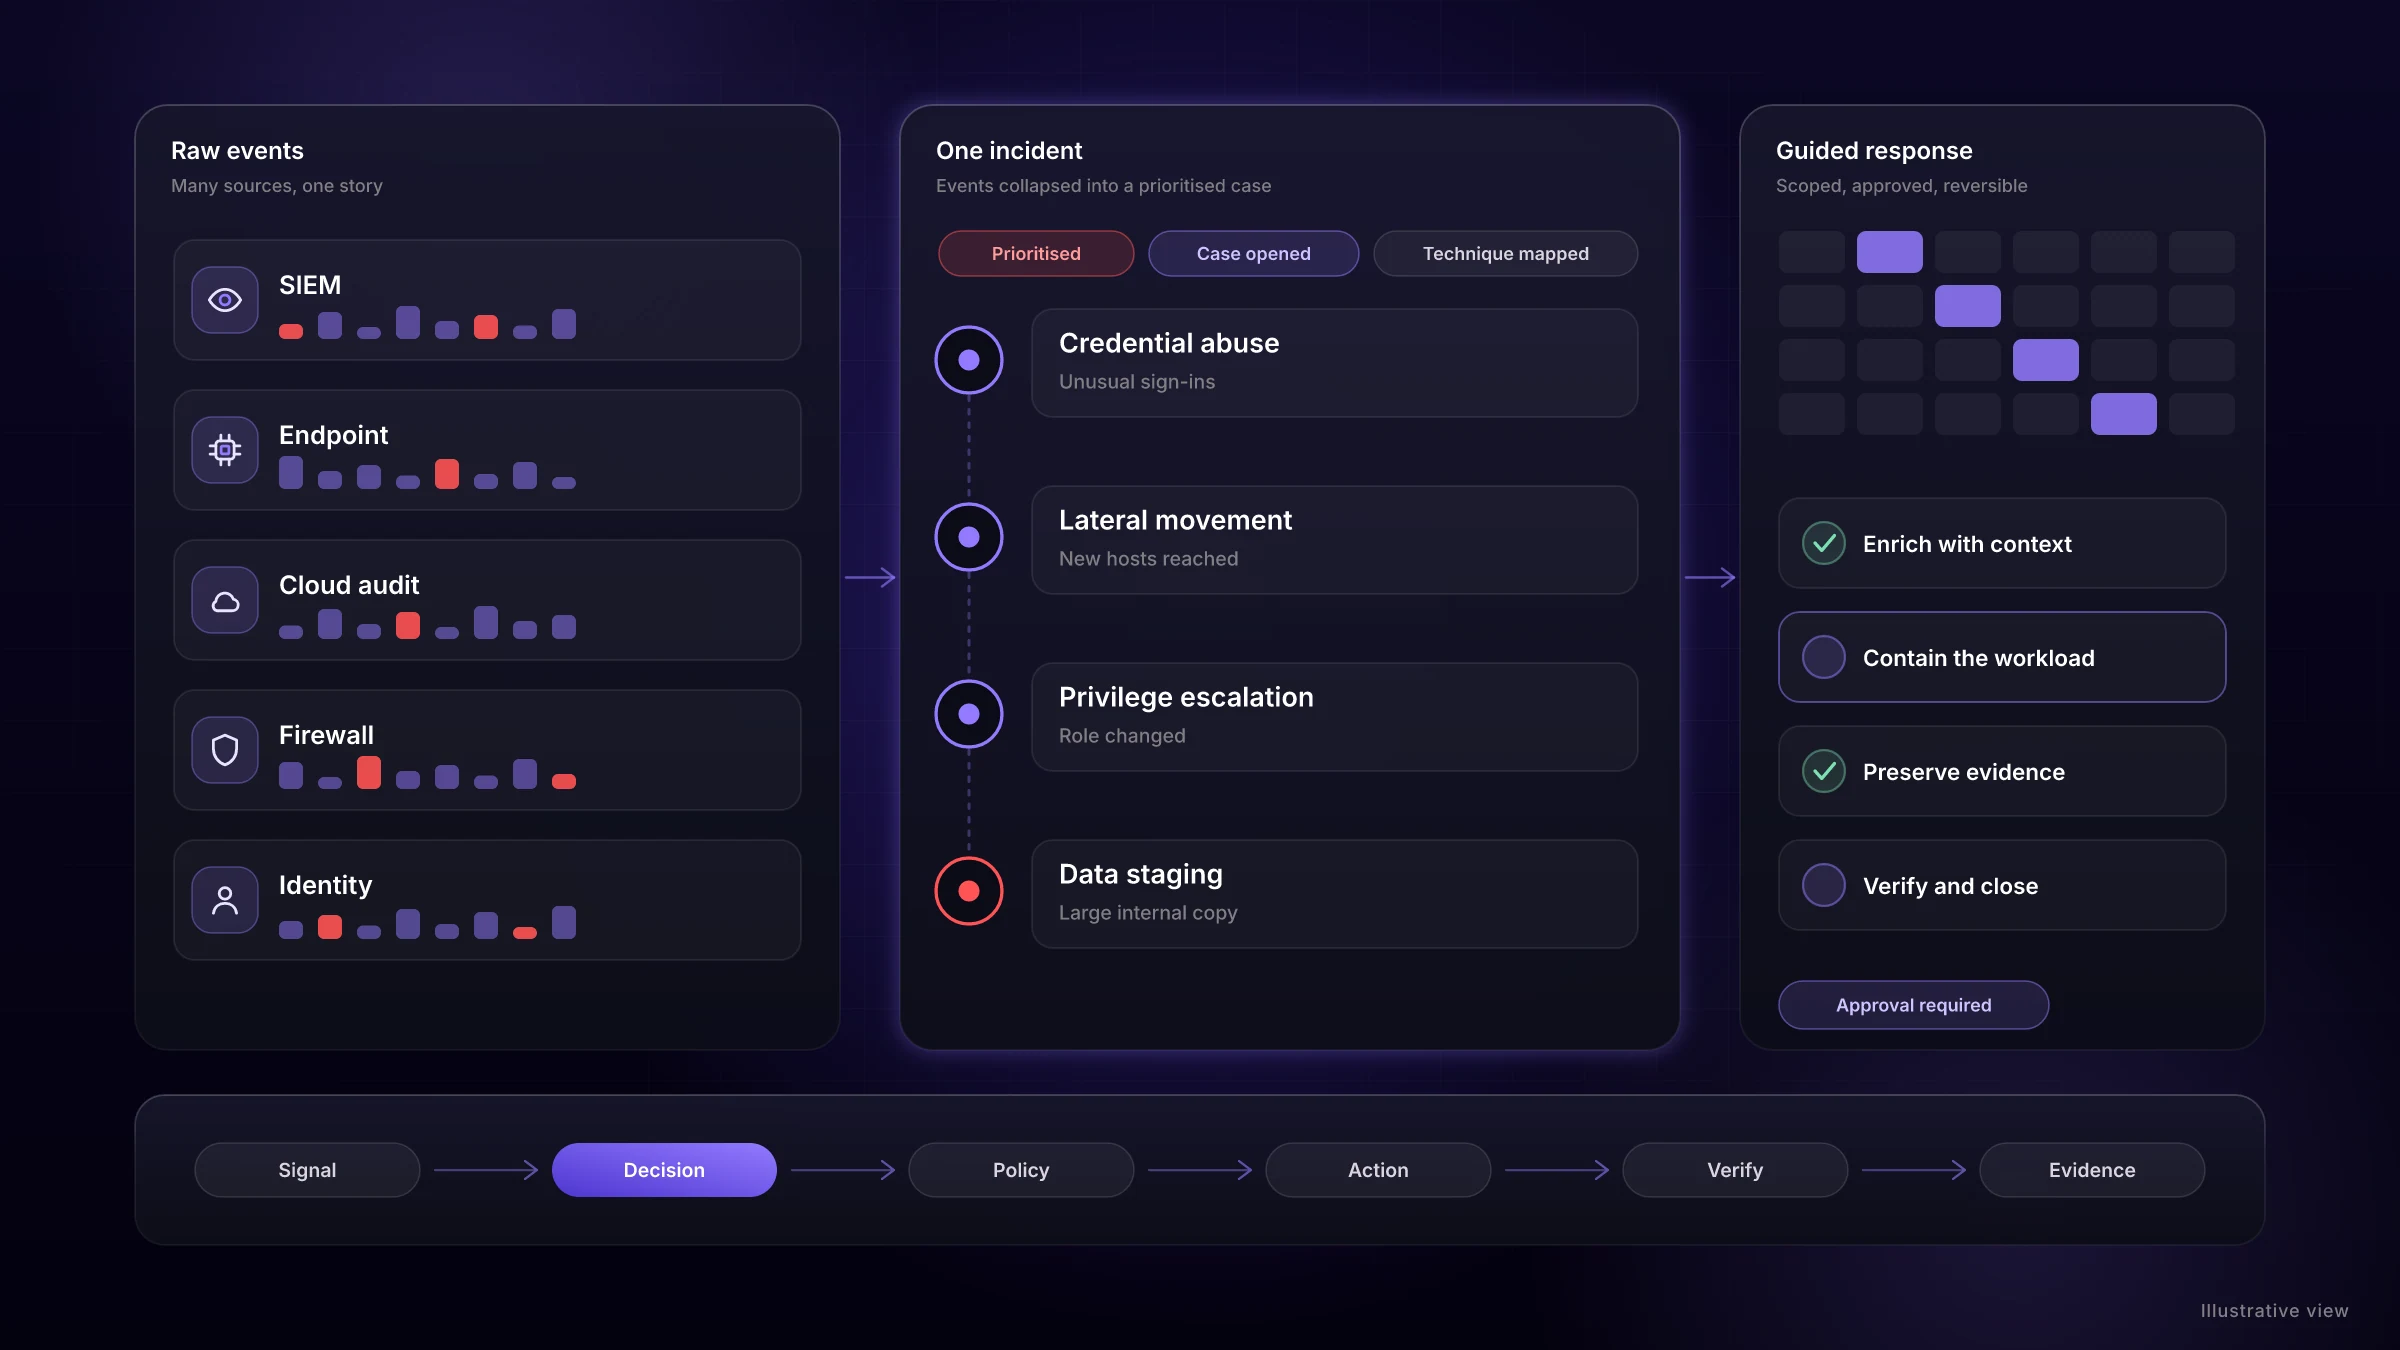
Illustrative view: raw events from SIEM, endpoint, cloud, firewall and identity sources become one prioritized incident with a guided response

Five Cybersecurity AIOps services

Each service can be taken alone. They share telemetry, policy and runbooks when combined.

SOC Threat Correlation & Incident Response

Turn SIEM, EDR, cloud, firewall and identity alerts into prioritized incidents with guided response.

Example scenario

Simulate credential abuse plus lateral movement and collapse the raw events into one incident.

Core capabilities

  • Security event normalization
  • Correlation
  • MITRE ATT&CK mapping
  • Case management
  • Enrichment
  • Response playbooks

Vulnerability Prioritization & Remediation

Rank vulnerabilities by exploitability, exposure, runtime context and asset criticality.

Example scenario

Ingest many findings and surface the few that are most urgent in context.

Core capabilities

  • Scanner ingestion
  • Asset context
  • CVE and EPSS interface
  • Attack-path context
  • SLA tracking
  • Remediation workflow

Identity & UEBA Detection and Response

Spot suspicious user and service-account behavior against learned login and privilege baselines.

Example scenario

Simulate an abnormal login and a privilege escalation, raise a UEBA incident and respond.

Core capabilities

  • Login analytics
  • Behavioral baselines
  • Impossible-travel simulation
  • Privilege-change detection
  • Risk scoring

Cloud & Kubernetes Threat Containment

Detect runtime and control-plane threats and apply tightly scoped containment.

Example scenario

Run a malicious-container simulation and quarantine the workload while preserving evidence.

Core capabilities

  • Runtime signals (Falco)
  • Kubernetes audit events
  • Cloud events
  • Identity context
  • Network-policy context
  • Containment policy

Phishing, Malware & Security Triage

Automate safe enrichment, classification and case creation for suspicious messages, files and URLs.

Example scenario

Submit a simulated phishing message, extract the IOCs and generate an investigation case.

Core capabilities

  • IOC extraction
  • Sandbox result parsing
  • Reputation connectors
  • Risk scoring
  • Analyst queue
  • Case summary

What you receive

Every service is built as a local-first lab, then extended to your private cloud and to AWS, Azure or GCP.

KPI dashboards

Ingestion health, processing latency, decisions, automation success and failure, overrides and false positives where measurable.

Runbooks and policies

Validated, allowlisted actions with approval rules and least-privilege identities.

Failure-path tests

Healthy, false-positive, policy-blocked, automation-failure, rollback and telemetry-source-failure cases, all exercised.

Audit evidence and demo

Retained evidence for every decision, a short demo script, and setup, troubleshooting and cleanup documentation.

Automation with guardrails, not blind trust

Rules every AIOps action follows, in every track.

Allowlisted actions only

AI output never goes straight to a shell, cloud API or cluster. It selects from validated runbooks.

Approval for high-risk change

Disruptive actions wait for a person. Low-risk, reversible steps can run on their own once you agree the rule.

Verified outcomes

Every action is followed by a health check, with rollback or compensation when the check fails.

Complete audit history

Signals, scores, model or rule versions, approvals and results are retained and reviewable.

Typical technology base

  • OpenTelemetry
  • Prometheus
  • Grafana
  • Loki / Tempo
  • Kubernetes
  • Helm
  • Terraform
  • Ansible
  • Argo CD / Rollouts
  • Python / FastAPI
  • PostgreSQL
  • Redis / NATS / Kafka
  • Trivy · Semgrep · Checkov

Adapted to the tools you already run.

Other AIOps tracks

Combine tracks to share telemetry, policy and runbooks.

Start with Cybersecurity AIOps?

Tell us what you run and where operations hurt most. We will suggest where to begin.

Talk to an AIOps Specialist

Stay in the loop

Blog posts, our newsletter and service updates on cloud migration, DevOps and reliability engineering, straight to your inbox.

We email you once to confirm. No spam, and we never share your address. Privacy Policy